22 September 2008

ECM Training from CMS Watch

CMS Watch recently released a new training program.  Their Fundamentals of Enterprise Content Management Technology aims to help educate organizations on ECM technologies.  The course has a broad focus from what "you're getting into" when implementing ECM technologies to how gather requirements (and a lot in between).  Even if you are working with  or plan to work with a consulting agency, it will greatly benefit your organization to be educated. 


From experience, educated clients are in a better position to make decisions about implementations than clients that have limited experience and/or education.  If you're considering implementing ECM technologies, I would highly recommend attending the course. 

29 August 2008

.NET Framework Service Pack Breaks SharePoint v2.0

Filed under the "be careful when updating servers" category, Microsoft announced on Wednesday that an update to the latest .NET Framework (v3.5) will cause problems with WSS v2.0 (and SharePoint 2003 by proxy). 

Anyone who has been working on SharePoint since the 2003 timeframe will probably remember that this is not the first time that framework updates have broken the previous version of SharePoint.  Most notably, when updating a SharePoint 2003 server to .NET 2.0, the index server mysteriously stopped indexing content.

This latest issue just reinforces the old adage that you need to thoroughly test updates in a non-production environment, even if Microsoft says they're O.K.

27 July 2008

SharePoint and Coffee ... Perfect Together

It's not clear what implication the following recommendation from Amazon may have, but I suspect that Rob Bogue et. al. will be thrilled with the additional promotion. 

image

In fact, the recommendation is a split -- promotion of products based on what I just ordered (K-Cups for my new coffee maker) and products that fit my purchasing habits over the last few months.  However, the presentation of the two recommendations together made for a remarkable checkout process.

24 July 2008

Take control of SharePoint Security

One challenge for companies implementing SharePoint is to figure out security. Keeping the model straight over time, as the SharePoint implementation matures, is even more of a challenge. SharePoint's ease of installation and high-level configuration can sometimes mask its underlying complexity, especially when dealing with more advanced scenarios like security.

Click here for the rest of the article on SearchWinIt.COM

16 July 2008

Integrating existing applications with SharePoint Server 2007

It's likely that you are using Microsoft Office SharePoint Server 2007 in your organization. If not, there's probably a strong contingent within your organization lobbying to implement the technology.

Once you have SharePoint server, though, there's the inevitable challenge of integrating existing applications into the portal framework. So, this begs the question -- if you want to use SharePoint as your enterprise portal platform, how do you integrate applications that aren't "SharePoint-aware?"


Read the rest of the my new article on SearchWinIT.COM

03 July 2008

SharePoint and Oracle Internet Directory (LDAP)

[UPDATE 6 SEPT 2010] The code has been posted on a new article about connecting SharePoint to Oracle LDAP

I have a client who recently wanted to leverage their Oracle Internet Directory server to authenticate users in SharePoint.  Since OID is LDAP compliant, I figured I could just use the generic LDAP provider with SharePoint.  Turns out, that provider is only supplied with MOSS and my client was using WSS.  So, off to Visual Studio to create a custom membership provider I went. 

I've seen a number of posts regarding the creation of custom membership providers for non-Microsoft directory sources like SunOne and OID.  However, I never saw any code samples (most folks didn't seem to be able to get it to work).  While other posts on custom membership providers tended to rehash the same material on SQL Membership.  As it turns out, it's pretty straight forward, as long as you have all of the right connection information (and understand the schema of the directory).  I would be happy to post the code if anyone is interested.  Short of that, here are some of the discoveries I've made:

  1. You can use the standard System.DirectoryServices.Protocols.LdapConnection class to connect to OID.  Here's the generic code I used:

    LdapDirectoryIdentifier _identifier = new LdapDirectoryIdentifier(ldapServerName, portNumber);
    connection = new System.DirectoryServices.Protocols.LdapConnection(_identifier);

  2. You need to override the Initialize member of the base membership class to supply the various connection settings you'll need.  There's a NameValue collection that's passed to this member built from the properties on the provider information you have to supply in Web.Config.  In my case, I limited my settings to LDAP server address (name or IP address), the LDAP port (originally my client suggested they used a non-standard port), Application Name (a property you must override when developing a custom membership provider) and LDAP domain (e.g. dc=com,  dc=customer).   The MOSS supplied provider is a bit more flexible, but I didn't particularly need all of that flexibility (read "complexity").
  3. I had to add the same provider information to Central Administration as I did for my SharePoint site.  I didn't change the authentication method on Central Admin, but without adding the provider, I could not get the people picker (in my SharePoint site) to resolve the user IDs from OID.  Once I added the provider all worked well.  In fact, in some cases, it seems that Central Admin "knows" about the user before the SharePoint application.
  4. You have to overload the following members in the base membership provider in order for it to work with SharePoint
    1. ValidateUser (the member that actually ensures the user is who they say they are)
    2. GetUser (both versions)
    3. GetUserNameByEMail
    4. FindUsersByName
    5. GetAllUsers

      An article published on MSDN defines the minimum interfaces: http://msdn.microsoft.com/en-us/library/bb975135.aspx#MOSSFBAPart2_DevelopingCustom
  5. You don't necessarily have to authenticate with the directory to exercise most of the members above, with the exception of ValidateUser.  In my case, my client's OID implementation enabled anonymous access.
  6. The act of "binding" to the LDAP directory validated the user.  That said, this only worked for users in the directory.  If I passed a user that did exist, but provided the wrong password, the validation failed as expected.  If, however, I passed a non-existent user to the directory (regardless of the combination of user ID and password), the Bind() method did not return any errors and my "authentication" worked.    I'm not sure if I've missed something or if this is unique to LDAP, but it was a strange behavior.  During my development I used a tool called LDAP Admin (http://ldapadmin.sourceforge.net/).  The tool was invaluable for validating connection information and user data.  It also, however, suffered the same fate as my code -if I tried to authenticate a user that didn't exist, the connection would be successful.  Weird.
  7. My client also wanted to use a single sign-on service provided by OID.  The service is quite flexible, supporting three different methods for supplying credentials to target applications - GET, POST and BASIC..  Unfortunately, since we configured the site with a custom membership provider, the only options were either GET or POST.  We chose post.  Unfortunately, the standard login page doesn't seem to want to allow a post from another page (although I didn't spend a long time to work it out).  I ended up constructing a basic page that took in form properties and then used the Membership class to authenticate the user and redirect them back to the SharePoint site.

Ultimately, the new provider works well and the SharePoint site is integrated with the SSO server.  User's who have access to my client's Oracle Portal can seamlessly access their SharePoint site as well  -- all without having to authenticate a second time.  And, because both web sites use the same LDAP, there's not need to synchronize user IDs and passwords.

Again, if you're interested in the code, just drop me a line; if I get enough requests, I'll post the code directly.

[UPDATE 6 SEPT 2010] The code has been posted on a new article about connecting SharePoint to Oracle LDAP

28 June 2008

REVIEW: Carbonite Online Backup

One of the challenges of constantly traveling is ensuring that all of my data is continuously backed up.  Having lost data as a result of either a hardware or software failure, I know I need a backup, but I could never find a good solution. Enter Carbonite.

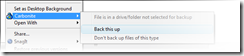
I happened upon Carbonite about four months ago.  Essentially, they offer an online backup of your machine (Windows only).  For $49/year, they will allow you to backup an unlimited amount of data.  When you sign-up for the service, they require a small agent download and install.  The agent constantly monitors various folders/files on your machine to determine whether they've changed; if they have, it starts copying the file to your online backup.  By default, Carbonite will backup all of your personal files -- on XP, this means anything in your Documents and Settings directory.  In Vista, this would include anything in your Users directory.  If you want to add other directories/files, just right click on the file or directory and pick Carbonite from the context menu and then "Back this up."  With virtually the same operation, you can also exclude certain files.
image

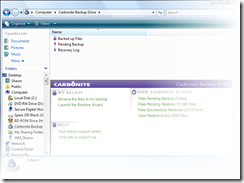
In addition, Carbonite surfaces in your "My Computer" as another drive.  Double clicking on the icon will show you what's been backed up.  It's presented as an Explorer-like interface, making finding a file pretty easy.
image

In my own experience, I ended up backing up about 32 Gb of data.  The complete backup took a number of days to complete.  However, Carbonite indicates a particular file's backup status by placing a small "button" on each file -- if the button is yellow, the file is in need of backing up.  If the button is green, the current version of that file is backed up.  You can also look at the Carbonite agent status in your system tray -- green indicates all files are backed up and yellow indicates that certain files require backup.

While backup is one thing, the restoration is entirely a different matter.  I also recently had the opportunity to test the service.  Not being completely trusting, I backed my files to a USB drive prior to wiping out my machine.  I then reloaded by then XP laptop with Vista, reloaded the Carbonite agent and told the agent to start a restore. 

Within a day I had most of my important files back.  That said, it's been about a week since I started the restoration and Carbonite still reports that I have quite a few files left to restore.  In truth, I'm not precisely sure what is missing, but I suspect it's my extensive (legal) music collection, since all of my documents have been restored.  Looking at the restore status in Carbonite has largely confirmed my theory.

My Observations:

  • While backups certainly can happen over a longer period of time, waiting a week (or more) to get all of your files restored is unreasonable.  Granted, I've not been connected to a high-speed connection the entire time.  However, I have had 1 Mb or better connectivity for the better part of four days during week.  I'm not sure if the slowness is simply a function of available bandwidth or how Carbonite prioritizes its use of your bandwidth; throttling bandwidth usage for normal backups is expected, but I would think it would want to consume as much bandwidth as possible for the restoration.
  • I've recently started using the service on a server.  I'm not backing up a ton of data, but the fact that the files are "instantly" offsite is somewhat comforting.  Because there isn't a lot of data AND the server will have a dedicated connection with loads of bandwidth, my guess is that any restore should be pretty snappy.
  • I have tried contacting support regarding my restore speed.  It's been two days and so far I've not heard back.  Their web site did state that they were dealing with "higher-than-normal" volume.  Not sure what that means for them, but I'm growing a bit impatient.

My Verdict:

  • For basic backups of your files, I've been pretty happy with the service.  For $49/year, you can't beat the price, especially since you're allowed unlimited space.
  • Now knowing restores take so long, you may consider just using Carbonite for selected files.  If you have  high-speed connection, the restore should be O.K.  My bread and butter files were restored pretty quick (desktop and documents).

If this service sounds interesting to you, check out Carbonite's web site.  (NOTE: the link is a "refer a friend link")